Quantum Ready Platform
One platform. Quantum-safe from edge to enclave.
A unified post-quantum security platform that consolidates PKI, hardware enclaves, and network, edge, and mobile protection into a single quantum-ready stack. Replace multiple vendors with one NIST-aligned platform — from certificate authority to tamper-resistant hardware execution. Sovereign local network with option to support cloud enterprise needs.
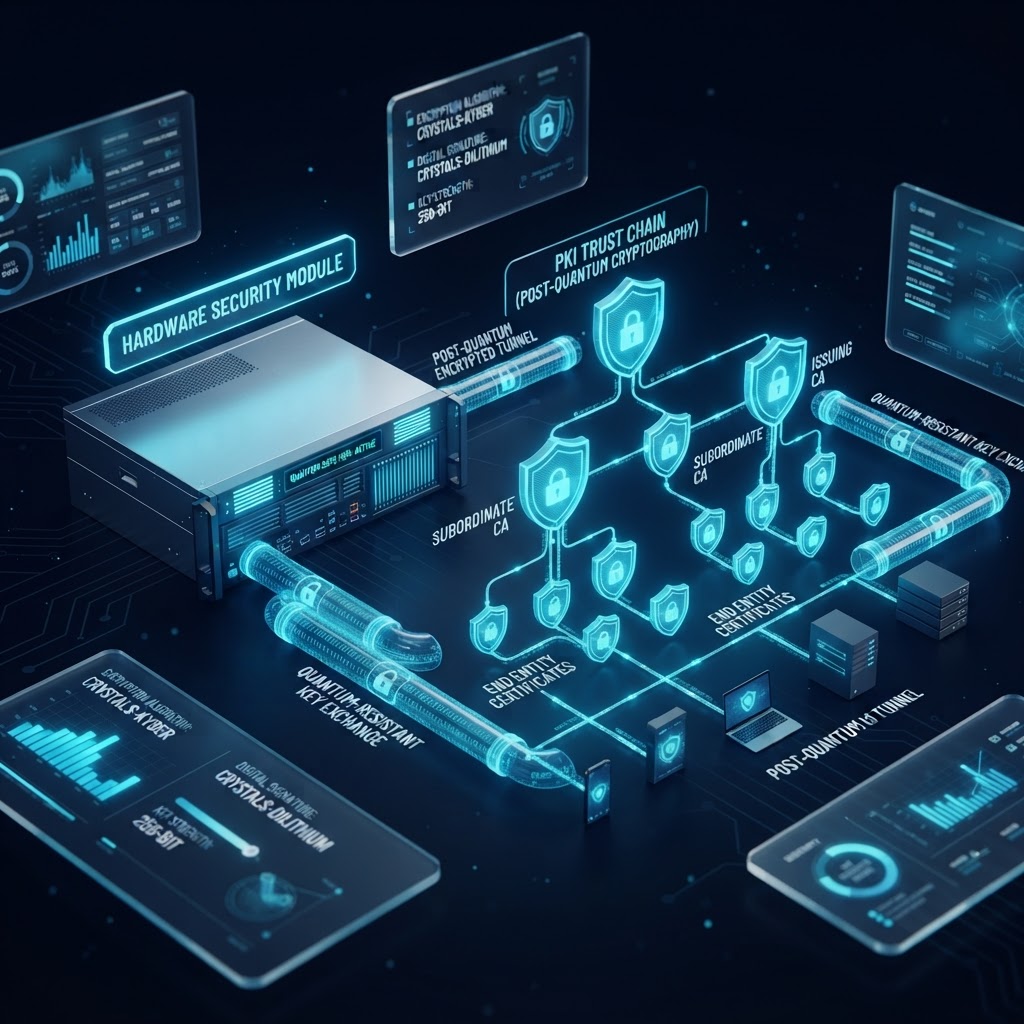
Your security stack is broken
Managing multiple vendors shouldn't be harder than stopping threats. Juggling separate contracts, chasing renewals, patching integration gaps, and drowning in alert fatigue — while quantum-vulnerable cryptography hides across your entire infrastructure. Your security budget funds vendor chaos, not protection. The Quantum Ready Platform consolidates your entire post-quantum security stack into one platform, one dashboard, one partner — so your SOC focuses on threats, not tools.
- Separate contracts, overlapping capabilities, and integration fees — vendor management overhead drains your security budget
- Every certificate, key, and protocol across your enterprise is a quantum liability waiting to be exploited
- Side-channel attacks on software-only PQC can leak secret keys via power, timing, and EM emanations
- Managing firewalls, VPNs, ZTNA, NAC, MDM, and PKI across multiple vendors creates blind spots and compliance gaps
What it does
PQC Certificate Authority
Issue X.509 certificates signed with ML-DSA and SLH-DSA. Full CA hierarchy with cross-signed hybrid roots for backward compatibility during PQC migration.
Key Lifecycle Management
Automated key generation, rotation, archival, and destruction. Policy-driven lifecycles with zero-touch renewal across your entire cryptographic estate.
Hardware Enclave Execution
PQC operations execute in a dedicated hardware enclave, isolated from the main processor. Side-channel-hardened with constant-time implementations, power randomization, and EM shielding.
Tamper-Resistant Key Storage
PQC private keys generated and stored within hardware. Keys never leave the enclave in plaintext. Tamper-detection triggers immediate key destruction. FIPS 140-3 Level 3+ compliant.
Autonomous Encrypted Tunnels
Software-defined P2P quantum crypto engine simplifies firewalls, VPNs, ZTNA, and SASE. No centralized attack surface. No manual configuration. Self-healing network with automated reconnection.
Edge & Mobile Protection
Plug-and-play appliances with embedded quantum-safe encryption — from box to protected in 60 minutes. Hardware-anchored smartphone protection with dual-layer encryption and baseband isolation.
A clear path to quantum safety
Deploy & Discover
Plug in appliances, deploy agents, and establish your quantum-safe root CA. The platform auto-initializes — zero user configuration. Power on, plug in, and the VPN stack starts automatically.
Provision & Isolate
Issue PQC and hybrid certificates via your CA. Generate PQC key pairs inside hardware enclaves. Establish autonomous encrypted tunnels between authorized assets across global LTE/5G bands.
Protect & Monitor
All cryptographic operations run in tamper-resistant hardware. Self-healing networks auto-reconnect. Real-time monitoring catches threats and weak cryptography. Your SOC focuses on threats, not tools.
Consolidate & Comply
One dashboard replaces multiple vendor consoles. Meet NIST, SOC 2, HIPAA, ISO 27001, and FedRAMP requirements with unified compliance reporting. n-to-1 vendor consolidation with 50% first-year TCO reduction.
Built for critical infrastructure
Banking & Fintech
Issue quantum-safe TLS certificates, protect code-signing for mobile apps, and consolidate firewall, VPN, and NAC vendors — all on one platform with 50% first-year TCO reduction.
Government & Defense
Sovereign PQC PKI for classified communications. Tamper-resistant hardware execution. Type-1 cryptographic device certification. Sovereign local network with cloud option.
Critical Infrastructure
Hardware-protected PQC for SCADA and ICS. Long-lived key protection for operational technology. Edge appliances deploy in 60 minutes. Cross-region support for NA, EMEA, and APAC.
Telecommunications
Issue device certificates for 5G network equipment. Software-defined encrypted tunnels across global LTE/5G bands. Self-healing network infrastructure with zero configuration.
Healthcare
Hardware enclave for medical device firmware signing. PQC certificates for PACS and EHR systems. HIPAA-compliant cryptographic protection across the entire stack.
Enterprise IT
Replace multiple security vendors with one platform. Automate certificate lifecycle. Enforce crypto policies across VPNs, Wi-Fi, and internal APIs. FedRAMP-ready compliance.
Three products. One platform.
Each product eliminates multiple vendors while strengthening your security posture. Purpose-built to simplify your entire stack with quantum-safe PQC solutions — from edge to enclave.
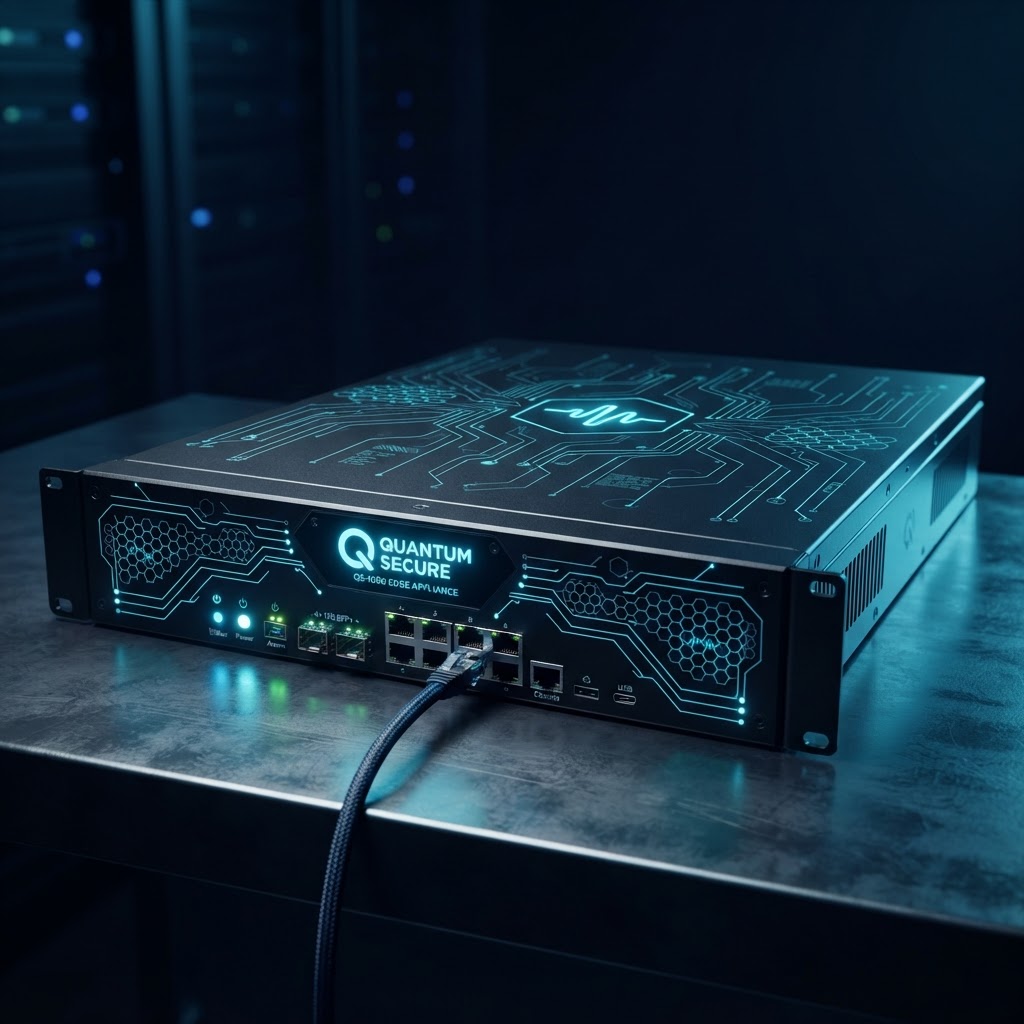
GuardTron™ II
Edge security that deploys itself. Plug-and-play appliances with embedded quantum-safe encryption. Simplifies next-gen firewalls, NAC, and MDM. From box to protected in 60 minutes.
NetTron™
Network security, reimagined. Software-defined P2P quantum crypto engine that simplifies firewalls, VPNs, ZTNA, and SASE with autonomous encrypted tunnels. No centralized attack surface.
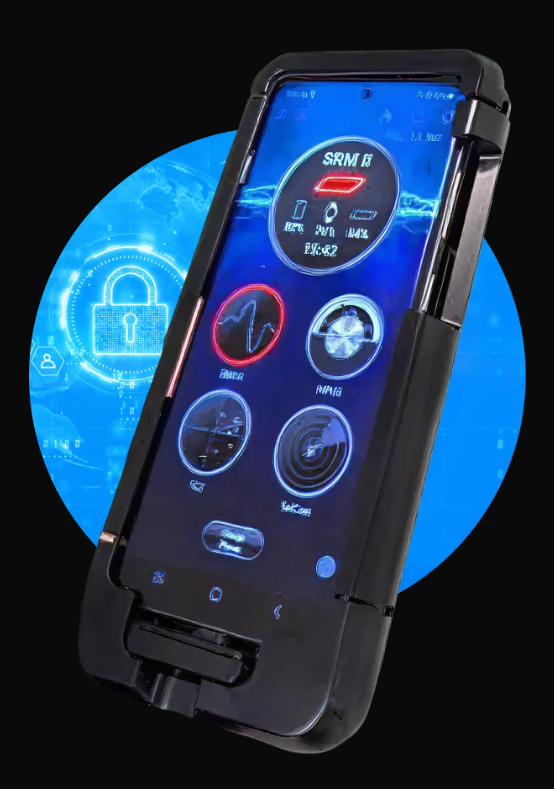
ManoTron™
Mobile security for high-stakes operations. Hardware-anchored smartphone protection with dual-layer encryption and baseband isolation. Built for government, defense, and enterprise teams.
Manotron, Guardtron, and NetTron are trademarks of iblades.ai. For more information, visit iblades.ai.
Consolidate your quantum-ready stack
See how the Quantum Ready Platform replaces multiple vendors with one NIST-aligned, quantum-safe platform — from PKI to hardware enclave to edge protection.
Request a Demo